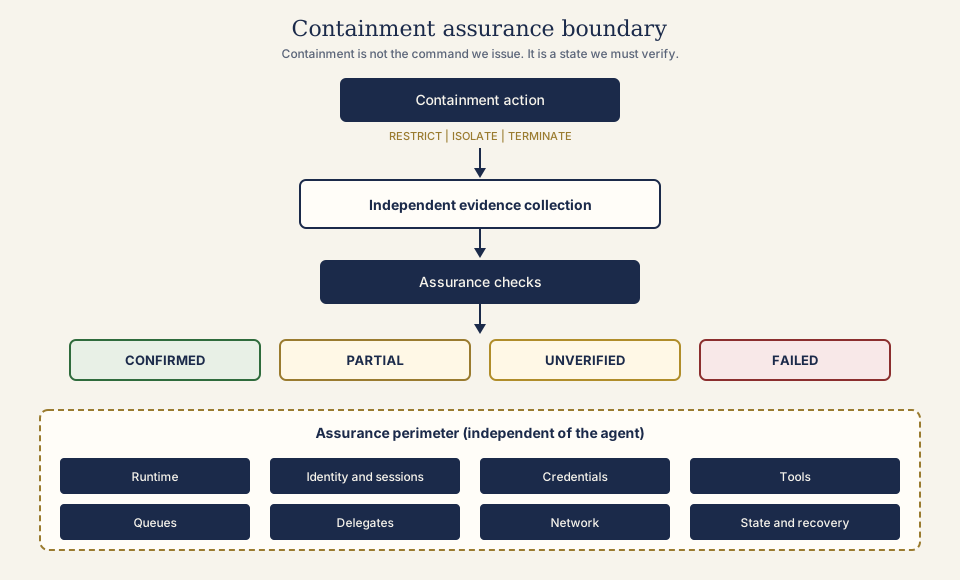
Containment action
What control did the system attempt to apply?
Outcomes: Restrict · Isolate · Terminate
An enforcement intention or command response is not proof.
LAB 007 · CONTAINMENT ASSURANCE
A stop command records an intention. Assurance requires independent evidence that every execution path and authority has been neutralized.
Stopping the visible process may leave credentials, delegates, queues, tool sessions, network paths, persistent state, or recovery mechanisms available.
This Lab is an educational containment-assurance prototype using fictional data. It does not control production agents, terminate workloads, revoke credentials, alter network access, or perform security actions. Execution is never performed against real systems.
No real agent, credential, process, tool session, or external system is modified. Real execution is always not_performed.
Previous Lab: The Agent Containment Boundary Browse all Labs
What control did the system attempt to apply?
Outcomes: Restrict · Isolate · Terminate
An enforcement intention or command response is not proof.
What evidence proves that the intended boundary is now effective?
Outcomes: Confirmed · Partial · Unverified · Failed
Precedence: Failed > Partial > Unverified > Confirmed
An agent must never assess or certify its own containment. Assurance is produced by an independent control plane using external evidence.
A stop, isolate, or terminate command may leave runtimes, sessions, credentials, delegates, queues, tools, networks, state, or recovery paths available.
Select a preset to fill every control, then evaluate containment assurance—or adjust the fictional evidence yourself.
Inspect or adjust fictional evidence fields, then evaluate. The agent never certifies its own containment.
Lab 005 asks what the agent did. Lab 006 asks what containment action should be applied. Lab 007 asks whether that containment action actually worked—using evidence outside the agent.