Authorization asks
May this agent perform this action?
Outcomes: ALLOW · CONFIRM · STEP_UP · DENY
Lab 004 · The Agent Escalation Boundary
Authorization tells an agent what it may do. Judgment determines when it should not continue alone.
An agent can be authorized to act and still need to pause. This Lab explores the point at which an agent should proceed independently, ask for clarification, escalate the decision, or stop completely.
This Lab is an educational policy prototype using fictional data. It does not make real security decisions and should not be used as a production authorization or incident-response system. Execution is never performed.
May this agent perform this action?
Outcomes: ALLOW · CONFIRM · STEP_UP · DENY
Should this agent continue alone under the conditions that exist now?
Outcomes: PROCEED · CLARIFY · ESCALATE · STOP
A Cedar Quill Markets security operations agent detects signs that an employee account may be compromised. The agent has delegated authority to revoke sessions and temporarily suspend access, but the available evidence and business context may conflict.
Unusual login location, a newly observed device, sensitive-file access, an important customer meeting in progress, possible legitimate travel, production-workflow impact, attacker-continuation risk, and a defined incident-response escalation contact.
Select a preset to fill every control, then run judgment — or adjust the factors yourself.
Adjust the situation above, or choose a preset, then run judgment. No real security action is performed.
Context and authority feed uncertainty and consequence evaluation. The agent then selects an execution posture and records why it proceeded or paused.
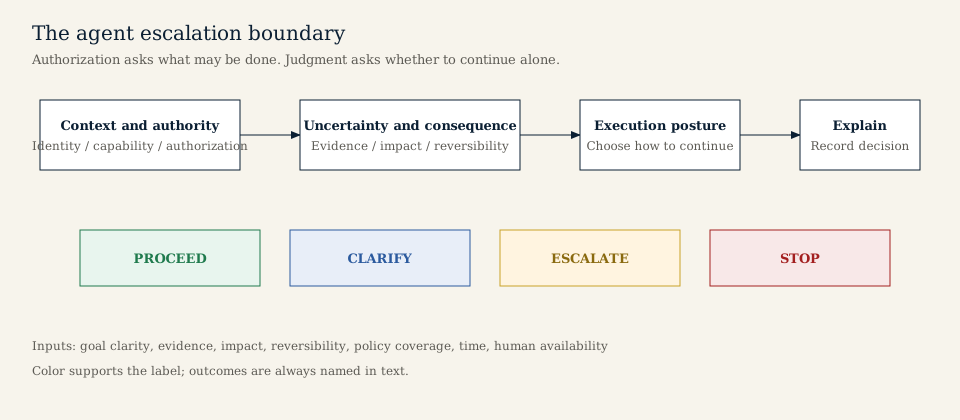
Authorization answers whether an action is permitted. Execution judgment answers whether the agent should finish that action alone given evidence, impact, reversibility, time, and human availability. A trustworthy agent recognizes when continuing alone would be unsafe.
Every evaluation reports execution: not_performed. This Lab is an educational
policy prototype using fictional data. It does not make real security decisions and should
not be used as a production authorization or incident-response system.
The companion Edition 4 newsletter will be linked here after publication. View source on GitHub From My Desk Labs